Citizen Lab links ad networks to spyware attacks
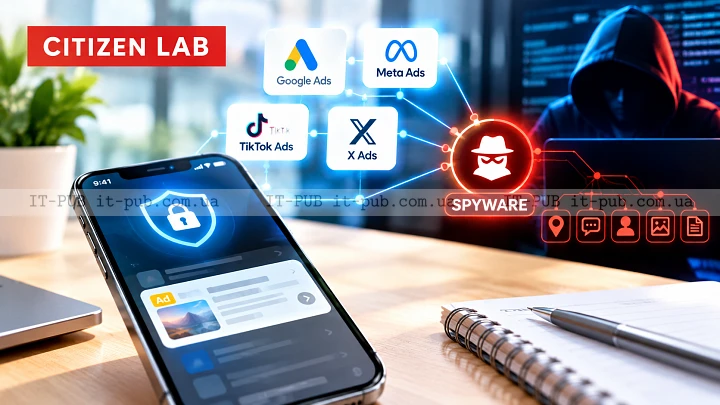
A new report says an Israeli ad platform helped deliver zero-click spyware, including attacks on Al Jazeera devices, through ordinary online ad systems.
Security researchers at The Citizen Lab say government spyware makers have found a new way to reach victims — by abusing online advertising networks. In a report published Thursday, the University of Toronto lab said an Israeli company called Discover-Tech helped spyware operators target specific people and devices with malicious ads, including attacks that could steal data without any click from the victim. According to IT-PUB News, Citizen Lab described this as the first confirmed case of zero-click, government-backed spyware being delivered through online ads. That gives the findings weight far beyond a single company or campaign.
The report matters because it points to a familiar part of the internet economy — ad targeting — as a possible delivery system for surveillance tools. Ad networks already reach huge numbers of phones, computers, websites and apps. If those systems can also be used to deliver spyware, the risk extends well beyond traditional phishing-style attacks.
Discover-Tech accused of connecting ad systems and spyware
Citizen Lab described Discover-Tech as presenting itself as a normal advertising company while acting as “a bridge between ad vendors and the mercenary spyware ecosystem.” The researchers said the company’s platform, called Controlium, was used by at least two spyware makers: Candiru and Bindecy.
Both companies make so-called zero-click spyware, meaning the software can infect a device without the user opening a message or tapping a link. That makes such attacks harder to notice and, in some cases, more dangerous than more familiar phishing campaigns.
The lab said the method relied on malicious online adverts served through global ad networks. In practice, that means the same systems used to place ordinary ads on websites and in apps can also be used to deliver code aimed at a specific target.
Al Jazeera devices were among the reported targets
One of the attacks examined by Citizen Lab affected at least 45 Windows computers at media organization Al Jazeera. The researchers said the devices were apparently hacked in 2024 and 2025 through Candiru spyware after being exposed to online ads containing malicious code.
Citizen Lab said it was not clear which governments were behind the attacks. Even so, the researchers argued that the case stands out because it shows how commercial ad infrastructure may be used to support spyware operations tied to state interests.
The report also said ad networks are attractive to attackers because they can reach almost any internet-connected device. That broad reach is part of what makes the abuse so troubling: tools built to help advertisers find audiences can also be turned toward highly targeted surveillance.
Exposed records gave researchers a view into Controlium
The researchers said Discover-Tech’s website exposed parts of its source code on login pages, allowing them to recreate the web-based control panel for Controlium without logging in. They said the dashboard appeared to be designed to let operators push malicious content to individual users alongside advertising.
Citizen Lab also found a publicly accessible section of the site that allowed them to download large volumes of user login records for the dashboard without a password. Some of those records reportedly belonged to at least two employees of Candiru, as well as some from Bindecy.
The researchers added that billions of ad bidding records were left exposed on Discover-Tech’s website. Those records showed that ads had been displayed across tens of thousands of mobile apps and websites between March and June 2026.
The data also suggested that the ads reached devices used by militaries, governments, critical infrastructure and national cyber agencies. Citizen Lab said it was not clear, however, whether those ad impressions led to any compromise or infection.
The report shows broad reach, but not the full scale
Citizen Lab said the case may be larger than the specific incidents it documented. Bill Marczak, a senior researcher at the lab, said there had been “a lot of buzz” about online ads being used to identify and automatically hack targets with precision, but that the report now provides concrete technical evidence that this can happen.
The researchers also worked with ad quality platform Confiant, which said it found evidence that potentially malicious ads were similarly shown on devices on the networks of the International Atomic Energy Agency and the International Criminal Court.
Even so, key questions remain open. Citizen Lab said it could not identify the governments behind the attacks, and it was not able to confirm whether every device exposed to the ads was actually infected. What the report does show is a sharper escalation of a known problem: malvertising appears to have been used to support stealthy spyware attacks.
Marczak urged defensive action, saying people who might be targeted because of who they are or what they do should disable ad tracking on their devices or block ads altogether. He said Discover-Tech is likely “just the tip of the iceberg.”
The companies named in the report did not offer responses. Al Jazeera did not reply to a request for comment, and neither did Discover-Tech. Integrity Labs, the maker of Candiru, could not be reached for comment.